CMMC Training
Learn CMMC Level 2 requirements, security controls, compliance obligations, and assessment readiness through self-paced practitioner-built training for defense organizations.

Prepare your defense organization for CMMC assessment with focused training on evidence collection, scope definition, security controls, SSP development, POA&M management, and assessor readiness. QMS Learning combines practitioner-built instruction, an AI compliance workbench, and audit-evidence tools to help teams build genuine capability, organize defensible documentation, and approach CMMC requirements with greater confidence.

Build practical CMMC capability through focused courses, cybersecurity pathways, and evidence-centered compliance tools.
Learn CMMC Level 2 requirements, security controls, compliance obligations, and assessment readiness through self-paced practitioner-built training for defense organizations.
Understand NIST SP 800-171 requirements and implement cybersecurity controls for protecting Controlled Unclassified Information while preparing for CMMC and government contract requirements.
Combine CMMC, NIST 800-171, ISO 27001, SOC 2, and data privacy training with AI-supported SSP drafting, POA&M building, and incident response preparation.
CMMC readiness requires more than completing training. Teams need a clear assessment scope, working knowledge of NIST SP 800-171 controls, organized evidence, and documentation that supports assessor review. QMS Learning connects role-specific instruction with an AI Workbench, Manager Dashboard, and Audit-Evidence Package export so your organization can develop capability, identify gaps, and prepare SSP and POA&M materials in a structured way.

See how practitioner-built training and evidence tools help regulated teams turn compliance knowledge into working capability.
QMS Learning combines practitioner experience, role-specific training, and evidence management in one platform.
Created by Will Trikha, a practitioner with over 20 years inside aerospace and defense compliance audits.
Export training records, completed scenarios, generated artifacts, and time-stamped activity as one evidence package.
Use AI-guided method selection for SSP drafting, POA&M entries, incident response, and compliance problem-solving.
Give CISOs, IT directors, compliance officers, and program managers shared tools that keep capability in-house.
Practitioner-led compliance training shaped by real audit and quality management experience.
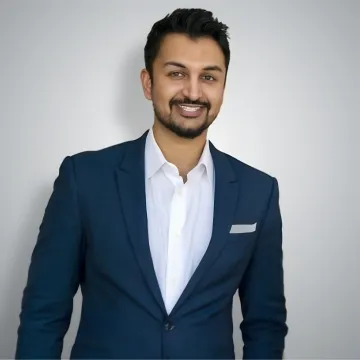
Founder
Will Trikha is the Founder of QMS Learning and a quality and operations practitioner with over 20 years of hands-on experience in regulated industries. Having written more than 1,000 findings as an auditor and closed twice that number as a quality manager, Will brings unmatched real-world depth to compliance training. His career has been built on the aerospace and defense audit floor, with deep expertise in AS9100D, ITAR, and related compliance frameworks. Frustrated by the persistent gap between conventional training and actual audit-ready capability, Will created QMS Learning to give quality teams the diagnostic judgment, AI-powered tools, and evidence management systems they need to walk into any audit with confidence. His practitioner-first philosophy shapes every course, pathway, and platform feature at QMS Learning.
A compliance audit evaluates whether an organization’s processes, controls, records, and practices align with defined requirements. For CMMC preparation, an audit or assessment helps identify gaps in cybersecurity controls, documentation, scope, and evidence. The goal is not simply to review policies, but to determine whether controls are implemented and supported by reliable evidence that an assessor can examine.
Talk with QMS Learning about your team’s assessment readiness needs.
Request a demo to see how QMS Learning supports evidence, scoping, training, and assessment preparation.
To help us assist you faster, please include the reason for your message so the relevant team can reach out as soon as possible.
To help us assist you faster, please include the reason for your message so the relevant team can reach out as soon as possible.